How ‘Spy Chips’ Breached Cold Wallets and Made Crypto Disappear
Summary
- An organized tampering attack targeting products from French hardware wallet maker Ledger led to reports of about $90 million in stolen assets.
- Custom components designed to intercept recovery phrases were inserted into genuine devices, allowing attackers to bypass the security chip while still passing authenticity checks.
- Cases involving Ledger, Coinkite and Trezor show that safeguarding digital assets is tied to risks spanning manufacturing, distribution, software and external services.
Forecast Trend Report by Period

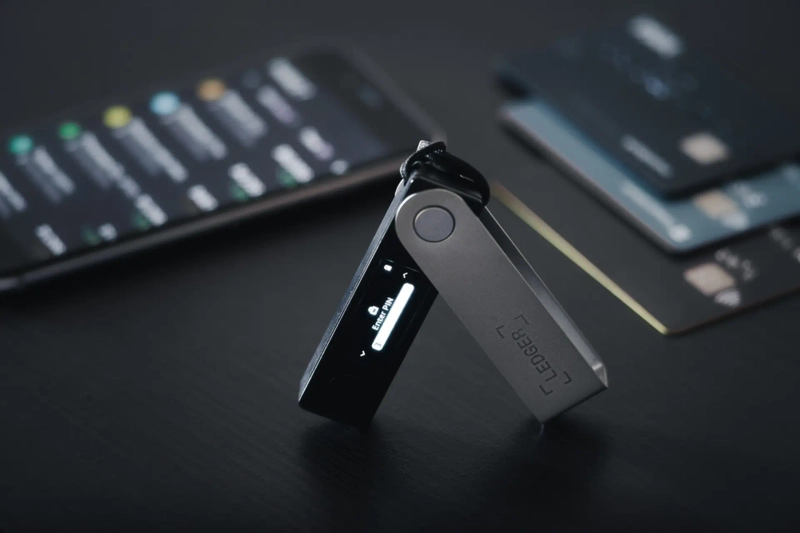
A hardware wallet bought to keep cryptocurrency safe instead became a conduit for theft. A criminal group opened the devices, hid malicious components inside and put them back into circulation. The case underscores how keeping private keys offline may not be enough to guard against risks in manufacturing and distribution.
Bloomberg reported on October 17 that complaints of asset theft tied to products from French hardware wallet maker Ledger began on October 9. Blockchain researchers estimate losses at more than $90 million. CryptoVilis, a Malaysian retailer identified in the investigation, has suspended operations. A notice dated October 10 posted at the entrance to its Kuala Lumpur store said it would close temporarily until further notice.
Ledger said in an official statement on October 15 that a highly organized criminal group inserted custom-made components into genuine devices. The attackers obtained the products over several months, altered them and distributed them through resale channels in Southeast Asia. The company said the group also built a server to collect recovery phrases, along with separate infrastructure to steal and launder assets.
The attack targeted recovery phrases displayed on the wallet screen. The phrase is critical information used to restore a wallet on another device if the original one is lost. The hidden component intercepted the phrase during the initial setup process and transmitted it externally over a mobile communications network. Attackers could then use it to restore victims' wallets and drain their assets.
The group did not need to hack the existing security chip directly. It bypassed the protections by using a separate device to read information being sent to the screen. Ledger said its security chip, operating system and servers were not compromised. Even so, the case exposed a weakness in which devices with tampered components could still pass existing authenticity checks even when the security chip itself was functioning normally.
Reports of suspected tampering also emerged from other sales channels. Ben York, who works in the cryptocurrency industry in Kuala Lumpur, said he found suspicious marks on the side of a Ledger Flex he bought at the MetaPod store at Singapore Changi Airport. The marks appeared to show that someone had tried to force open the back of the device.
York sent the device to Mark Karpeles, the former chief executive officer of Mt. Gox who now runs Tibanne Labs. Karpeles said he found a custom connector attached to the screen, along with a mobile communications chip and a SIM card. "This is not something an individual put together in a garage," he said, adding that it was "on the scale of something you'd see in a spy movie." Ledger said it is also reviewing tampering reports involving products bought from other sellers.
This is not the first security incident involving hardware wallets. Earlier, software flaws in products from Coinkite were estimated to have led to the theft of about $130 million worth of Bitcoin. Trezor also exposed the personal information of about 67,000 customers after a leak involving a delivery company. Asset theft and personal data leaks are different types of incidents, but both show that security weak links can extend beyond the device itself to software and external services.
Esme Pao, head of capital markets and policy at CertiK, said safeguarding digital assets is tied not only to cryptography but also to operational risks across the broader process. Failsafe Chief Executive Officer Enerlyn Flynn said blocking one type of attack does not mean other risks disappear.
Ledger has asked official sales and distribution partners in Southeast Asia and Hong Kong to suspend sales, and is investigating the matter with local law enforcement authorities. The company has also banned the resale of returned products and tightened distribution controls so stores keep devices separately and hand them over only at the time of purchase.
Doohyun Hwang
cow5361@bloomingbit.ioKEEP CALM AND HODL🍀