
PiCK
South Korea FSS Chief Orders Sector-Wide Security Review, Including Crypto Firms, to Block Access if Flaws Found
Summary
- The head of the Financial Supervisory Service said he had ordered stronger security inspections across the financial sector, including virtual-asset service providers, in response to a string of hacking incidents.
- He said outside access should in principle be blocked until security vulnerabilities are fixed if there is a risk of fund outflows from a cyberattack.
- The Financial Supervisory Service said it would take stern action over failures to follow security guidelines and urged management to expand next year’s security budgets and specialist staffing.
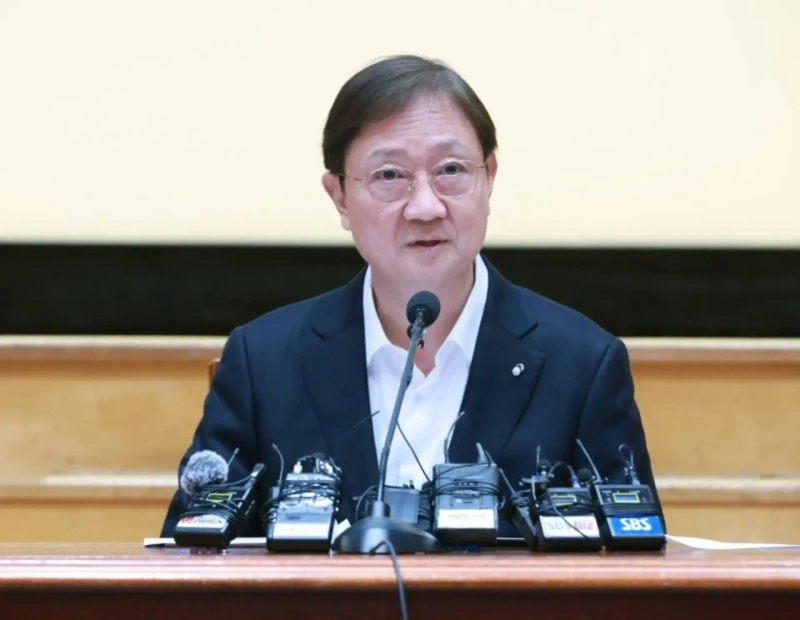
Lee Chan-jin, governor of South Korea’s Financial Supervisory Service, ordered tighter security checks across the financial sector, including crypto businesses, in response to a string of hacking incidents.
The FSS said on November 3 that Lee was briefed at an executive meeting that day on the cyberattack response status across financial industries. He then instructed officials to conduct a full inspection of security vulnerabilities in financial systems accessible from outside.
The review will cover not only traditional financial firms such as banks, brokerages and insurers, but also virtual-asset service providers, consumer lenders, online investment-linked finance companies and even businesses not subject to the Electronic Financial Transactions Act. The move follows the spread of hacking incidents across the financial sector, with some virtual-asset service providers and online investment-linked finance companies suffering actual monetary losses.
The regulator will first examine external access routes linked to systems that manage customer assets or financial companies’ own assets. Where a cyberattack could lead to a fund outflow, outside access is to be blocked in principle until the security vulnerability is resolved.
The FSS plans to deploy IT specialists to verify inspection results submitted by financial companies and check whether follow-up measures are being carried out. It will take stern action if it finds that existing security guidelines were not properly followed or that self-inspections were conducted only as a formality.
The agency also plans to strengthen accountability for senior management at large financial firms. If an incident occurs at comprehensive financial investment businesses or insurers because of inadequate basic security controls, the regulator will hold management, including the chief executive officer, accountable, as it already does in the banking sector.
Lee said IT security is a core factor determining customer trust and the sustainable operation of financial companies. He called on management teams and boards to take an active role in expanding next year’s security budgets and specialist staffing.
The FSS also plans to establish a dedicated internal security unit and expand related specialist hiring to strengthen the financial sector’s ability to respond to cyber threats.

Suehyeon Lee
shlee@bloomingbit.ioI'm reporter Suehyeon Lee, your Web3 Moderator.